Magento and Adobe Commerce technical audit.

A written picture of the store you have, and the first five things to do about it.

A read-only technical audit of a Magento Open Source, Adobe Commerce or Mage-OS store: release, PHP, extensions, performance, exposure and integrations, written up with a prioritised plan you own. For merchants who have inherited a store or want a second opinion before spending. The price is agreed in writing before we start.

For
Merchants who have inherited a store, or face an upgrade, migrate or rebuild decision
What it is
Six areas read from inside the store, with severities and a prioritised plan
Price
Agreed in writing before we start
First step
The free health check, then read-only access for the audit

Why merchants ask for an audit.

Three situations we hear about every month.

  • We took over the store from another agency and nobody can tell us what is in it.

    What it usually means

    Nobody has read it end to end. Until someone does, every estimate is a guess and every change a risk.

  • We have one quote for an upgrade and one for a rebuild, and they are miles apart.

    What it usually means

    Neither has been checked against the store. An audit tells you which job the store actually needs.

  • The store is slow and we do not know whether it is the hosting, the theme or the extensions.

    What it usually means

    It is usually a mix, and measuring is cheaper than guessing. The audit names the slow parts and their causes.

What the audit reads and reports.

Six areas, each read from the store itself, each written up in plain words with a severity and a recommendation.

  • Release, patch state, PHP and server

    Where the store sits in Adobe's calendar, PHP end of life, and the database, search, cache and queue.

  • Extensions and their support status

    Every module with its vendor, version, maintenance state and whether it is actually used.

  • Performance, measured

    Server response, field and lab data, cache hit rates, indexers, cron, and the queries behind the slow pages.

  • Security headers and exposure

    Reachable admin and API paths, two-factor, the edge in front of the store and any sign of past compromise.

  • Integrations

    Payment, shipping, ERP, marketing, search and feeds: how each connects and which are erroring today.

  • A prioritised plan

    Everything ordered by risk and cost, the first five things to do, and an honest view on upgrade, Hyvä or migration.

The same store, with and without us.

Without us
  • Quotes compared without anyone reading the store
  • Extensions nobody can name, still loading on every page
  • Performance blamed on the host, the theme or the weather
  • Exposure found by an attacker rather than by you
  • Integrations failing quietly in the logs
  • A big decision made on a hunch
With Refined Commerce
  • One document that says what the store contains
  • Every extension listed with its status and fate
  • Slow pages measured and their causes named
  • Exposed paths and missing controls listed with fixes
  • Every integration checked, with live errors flagged
  • A prioritised plan you own and can act on with anyone

Proof, from real stores.

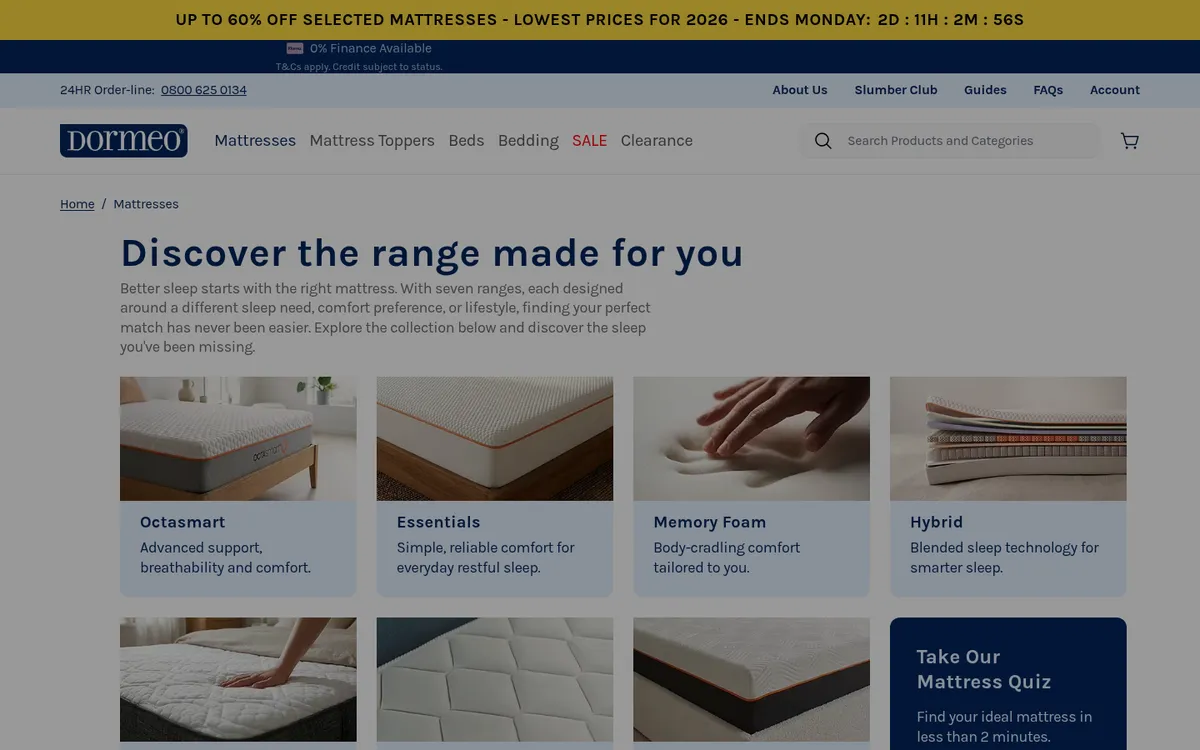
Dormeo: a category page of the live store on desktop
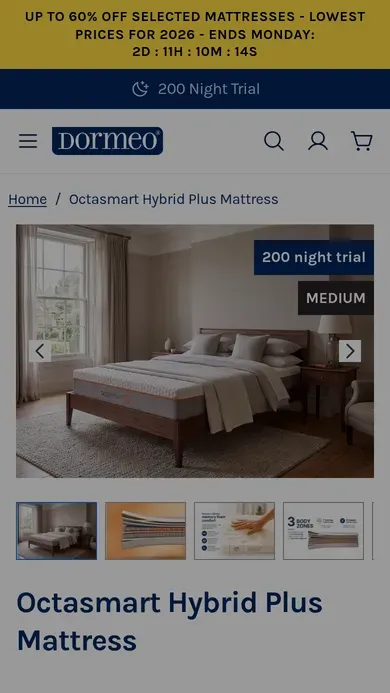
Dormeo on a phone
Mattresses and bedding, UK and IrelandMagento 2 and Hyvä

Dormeo

Hyvä build for dormeo.co.uk and dormeo.ie, with a continuing programme of consent, tracking and security work.

Passes Core Web Vitals on mobile
  • LCP1.5 s
  • INP138 ms
  • CLS0.03

Core Web Vitals, real-user data (Chrome UX Report), mobile, 28 days to 31st October 2026. Marks show Google's thresholds.

Rowan and his team have been excellent at website development. He is extremely responsive and goes above and beyond to achieve the desired goal. …

Anastasia LaskarisGoogle review

How we carry out an audit.

Read-only throughout. Nothing on the live store changes while we look.

  1. Step 1: The free health check

    Send us the store address. A senior engineer reads its release, support status, PHP, headers, hosting and any sign of a hijack.

    Within two working days
    Access we need
    None. Publicly served pages only; nothing is tested.
    What you receive
    One page by email, with no obligation.
  2. Step 2: Access and scope agreed in writing

    We list the read access we need, confirm what the audit covers and agree the price before we start.

    Day one
    Access we need
    Read-only: repository, admin account, hosting panel and logs.
    What you receive
    A written scope and price, before any work is done.
  3. Step 3: The store is read from the inside

    Code, configuration, extensions, database, server, logs and scheduled tasks, read by a senior engineer, with findings recorded against each area.

    Most of the audit
    What you receive
    Anything urgent reported to you the same day.
  4. Step 4: The slow and exposed parts are measured

    Performance measured on the pages that earn money. Headers, reachable paths and the edge checked from outside, read-only, with your knowledge.

    Alongside the reading
  5. Step 5: The report, and a call to walk through it

    Findings by area with severities and recommendations, and the prioritised plan at the front.

    On delivery
    What you receive
    One written document you own, and a call with us to go through it.

How is this different from the free health check?

Both are written by a person. One reads the store from the pavement; the other goes inside with your keys.

Free health check

  • Publicly served pages only, no access
  • Release, support status, PHP, headers, hosting, hijack indicators
  • One page, by email, within two working days
  • Free, no obligation
  • Cannot see extensions, code, database or integrations
About the health check

Technical audit

  • Read access to code, admin, server and logs
  • All six areas, including extensions, performance and integrations
  • A written report with a prioritised plan, and a call to walk through it
  • Price agreed in writing first
  • A document you own and can act on with anyone
Ask about an audit

We price the work, not the clock.

This service
Priced as a project: a written estimate once we have examined the store.
How you pay
Usually spread across the length of the project.
Our rate
£80 an hour plus VAT, the same for every merchant.
Never charged
Account management, or the first look at your store.

One price, agreed before we start.

An audit is priced as a whole. We tell you the price in writing before we begin, based on the size and shape of your store, and it stays the same unless you ask for the scope to change. No figure appears here because a single-store catalogue and a multi-store estate with an ERP behind it are not the same job.

  • Price agreed in writing before the audit starts
  • Read-only: nothing on the live store changes
  • You own the report and can act on it with anyone
What happens first
  1. We confirm the read access works and take a copy of the module list and configuration.
  2. Release, patch level and PHP are read and placed against Adobe's calendar.
  3. Anything urgent, such as a sign of compromise, is reported to you the same day.
How our pricing works

Is this the right service for your store?

This is for you if

  • You have inherited a store, or are unhappy with the current arrangement
  • You face a choice between upgrading, moving to Hyvä, migrating or rebuilding
  • You want a document your own team or another agency can work from
  • You use Magento Open Source, Adobe Commerce or Mage-OS

If your situation is different

Why merchants bring this work to us.

About Refined Commerce
  • 2008

    On Magento since its early releases

    Decades of collective experience across Magento 1, Magento 2, Adobe Commerce, Hyvä and Shopify. Very little about your store will be new to us.

  • 1

    Point of contact, and senior engineers only

    You deal directly with the founder. No juniors learning on your store and no account managers between you and the people doing the work.

  • 5.0

    On Google, from 23 merchant reviews

    Small stores and large ones, described in their owners' words. The reviews are quoted on this site word for word.

Questions merchants ask about this.

What access do you need for the audit?

Read access, and nothing that changes the store: the code repository or a copy of the codebase, a read-only admin account, and read access to the server or hosting panel so we can see PHP, the database, logs and scheduled tasks. Where a staging copy exists we use that for anything that has to be executed. Nothing changes on live during an audit.

Is this the same as the free health check?

No. The free health check reads only what your store already shows the world, on one page, with no access. The audit goes inside: code, configuration, extensions, database, server and integrations, and ends with a prioritised plan. The health check tells you whether to worry; the audit tells you what to do.

Will you just use the audit to sell us the fixes?

The plan is written so that anyone competent can act on it, including your in-house team or another agency, and you own the document. We are happy to estimate the work it describes, and we would rather you chose us because the audit was good than because it was vague.

Can you audit a store that another agency or a freelancer built?

Yes, and that is the most common reason we are asked. An audit is the right first step when you have inherited a store, are unhappy with the current arrangement, or want a second opinion before a large spend. We report what we find without editorialising about who built it.

How is an audit different from a security scan?

A scanner tests a store from outside and produces a list. An audit reads it from inside, puts each finding in the context of your release, extensions and hosting, and says which five things matter first. Security is one of six areas, not the whole.

What happens after the audit?

You get the written report and a call to walk through it. From there you can act on the plan yourselves, ask us to estimate any part of it, or put the store on a support retainer and work through it month by month. Nothing in the audit commits you to anything further.

What does a Magento audit cost?

It depends on the size and shape of the store: a single-store catalogue and a multi-store estate with an ERP behind it are different jobs. We tell you the price in writing before we begin, and it does not change afterwards unless you ask for the scope to change.

Can you audit a Magento 1 store?

Yes. For a Magento 1 store the audit also lists every extension and customisation with its Magento 2 equivalent, which is the groundwork for a Magento 1 to Magento 2 migration.

Start smaller: the free health check reads what your store already shows.

Before an audit, see what the store tells the world: release, support status, PHP, headers, hosting and any sign of a hijack, on one page, by email, within two working days. Nothing is accessed or tested, and no obligation follows.

  • Magento Open Source, Adobe Commerce and Mage-OS stores
  • No login, no access, no obligation
  • Written by a person, not a scanner
Free store health checkOne page, by email

5.0 from 23 Google reviews

Free, with no obligation. We read only what your store serves publicly; nothing is accessed or tested, and it is not a security guarantee. Privacy notice.
What you receive
Example report
Magento Security and Upgrade Health Check
example-store.co.ukNeeds attention
Platform
Magento Open Source 2.4.4-p3
Adobe support
ended 12th April 2025
PHP
8.1, end of life 31st Dec 2025
Frontend
Luma
Security headers
2 of 6 present
Hijack indicators
none found

What we would do first. Apply the outstanding security fixes, then plan the upgrade to a supported release.
Free health check